Vertex — security and access
Principles: least privilege per environment · no inbound internet exposure · the vendor can reach stage only · no credential with deploy rights exists in the vendor-writable repository.
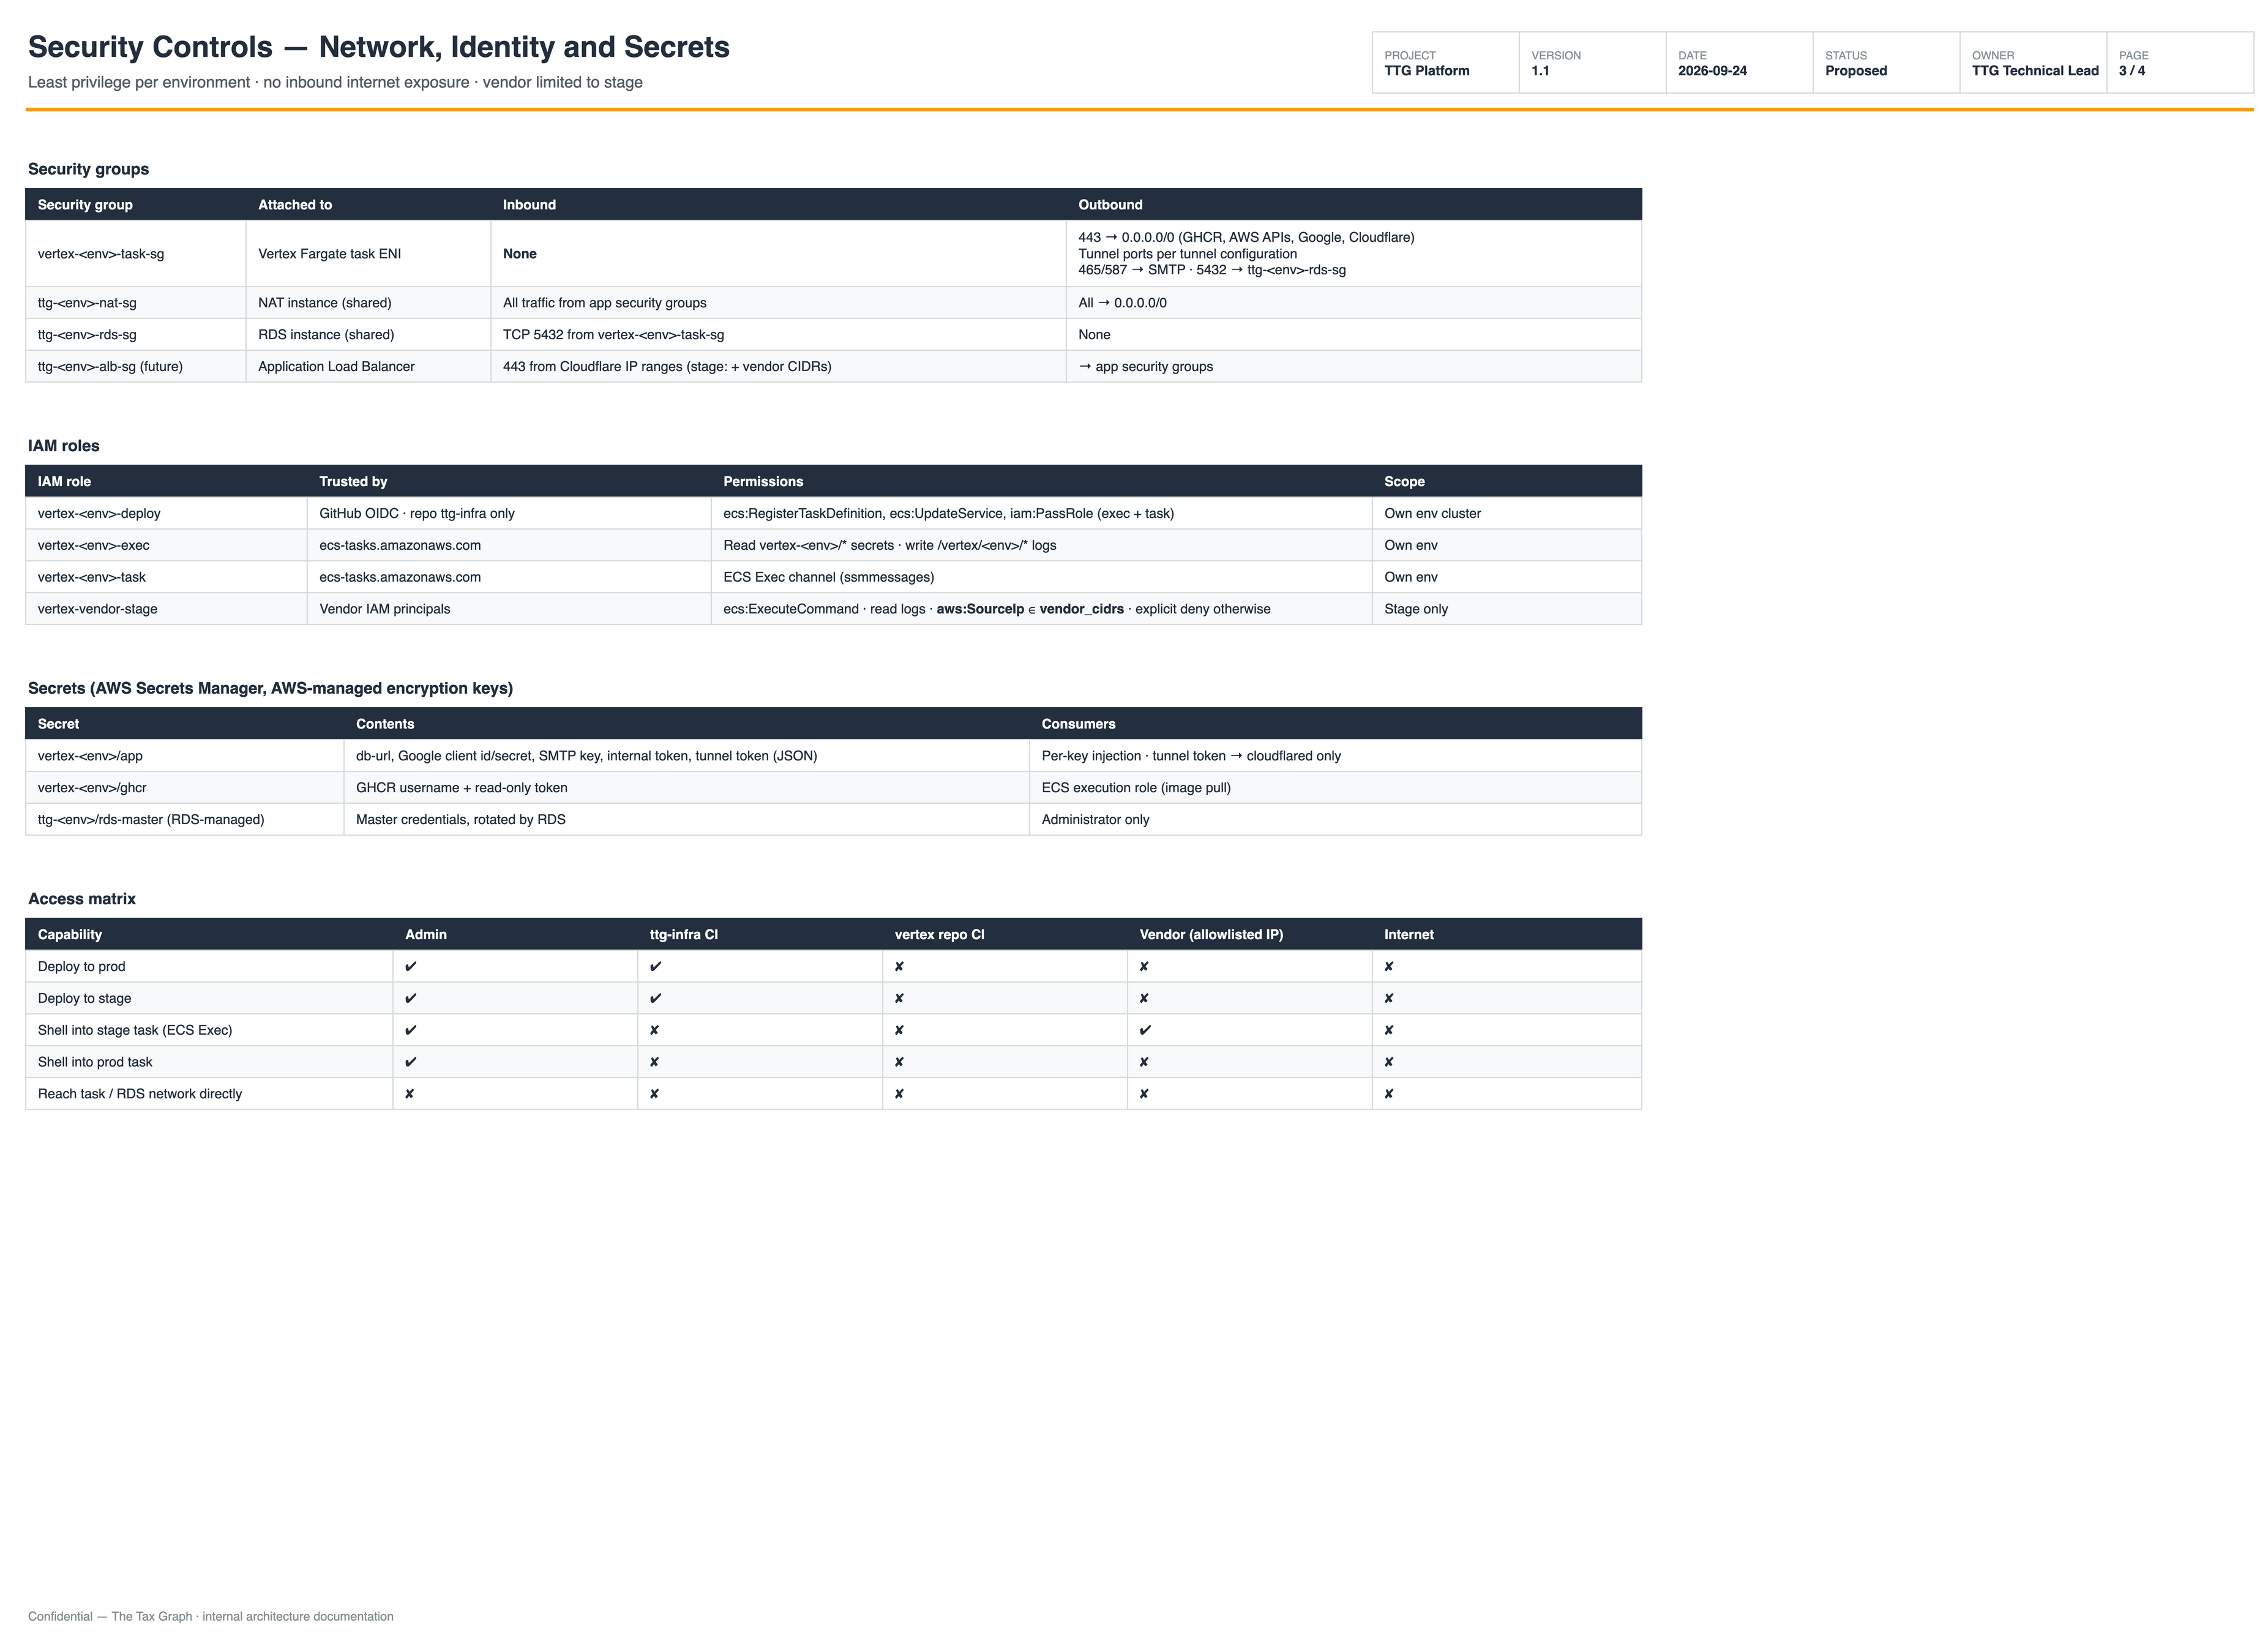
Security groups (identical shape per environment)
| Security group | Attached to | Inbound | Outbound |
|---|---|---|---|
vertex-<env>-task-sg | Fargate task ENI | None | 443 → 0.0.0.0/0 (GHCR, AWS APIs, Google, Cloudflare) · tunnel ports per tunnel config · 465/587 SMTP · 5432 → ttg-<env>-rds-sg |
ttg-<env>-nat-sg | NAT instance | All from vertex-<env>-task-sg | All → 0.0.0.0/0 |
ttg-<env>-rds-sg | RDS instance | 5432 from vertex-<env>-task-sg | None |
ttg-<env>-alb-sg (future) | ALB | 443 from Cloudflare IP ranges (stage: + vendor CIDRs) | → vertex-<env>-task-sg |
A security group cannot allowlist vendor IPs for tunnel or ECS Exec traffic, because both are initiated
outbound from AWS. Vendor IP control is therefore enforced in Cloudflare (stage hostname) and IAM
(aws:SourceIp).
IAM roles
| Role | Trusted by | Permissions | Scope |
|---|---|---|---|
vertex-<env>-deploy | GitHub OIDC, repo ttg-infra only | ecs:RegisterTaskDefinition, ecs:UpdateService, iam:PassRole (exec + task roles) | Own env cluster |
vertex-<env>-exec | ecs-tasks.amazonaws.com | Read vertex-<env>/* secrets, write /vertex/<env>/* logs | Own env |
vertex-<env>-task | ecs-tasks.amazonaws.com | ECS Exec channel only | Own env |
vertex-vendor-stage | Vendor IAM principals | ecs:ExecuteCommand, read logs, condition aws:SourceIp ∈ vendor_cidrs with explicit deny otherwise | Stage only |
No AWS role trusts the vertex repository.
Secrets (AWS Secrets Manager, AWS-managed keys)
| Secret | Contents | Consumers |
|---|---|---|
vertex-<env>/app | JSON: db-url, Google client id/secret, SMTP key, internal token, tunnel token | Injected per key; the tunnel token goes to cloudflared only |
vertex-<env>/ghcr | GHCR username + read-only token (classic PAT, read:packages) | ECS execution role (image pull) |
ttg-<env>/rds-master (RDS-managed) | Master credentials of the common RDS instance | Administrator only |
Access matrix
| Capability | Admin | ttg-infra CI | vertex CI | Vendor (allowlisted IP) | Internet |
|---|---|---|---|---|---|
| Deploy prod | ✔ | ✔ | ✘ | ✘ | ✘ |
| Deploy stage | ✔ | ✔ | ✘ | ✘ | ✘ |
| Shell into stage task | ✔ | ✘ | ✘ | ✔ | ✘ |
| Shell into prod task | ✔ | ✘ | ✘ | ✘ | ✘ |
| Reach task / RDS network directly | ✘ | ✘ | ✘ | ✘ | ✘ |